Ransomware evolution reveals attackers infiltrate systems long before encryption phase begins

The modern landscape of cyber warfare has shifted significantly, moving away from the "smash-and-grab" tactics of early ransomware iterations toward a more sophisticated, stealth-oriented approach that prioritizes long-term persistence within a victim’s network. A comprehensive study conducted by ITSEC Asia, detailed in their latest whitepaper titled "From Sample to Signal: Uncovering the GodDamn Ransomware Operation," has shed light on this alarming trend. The research highlights that the deployment of ransomware is merely the final, loud act in a silent, multi-stage performance that often unfolds over weeks or months.
For organizations worldwide, the traditional perception of ransomware—as a malware variant that instantly encrypts files upon infiltration—is increasingly obsolete. Instead, cybersecurity professionals are now facing advanced persistent threats (APTs) that treat ransomware deployment as the final stage of a larger campaign involving reconnaissance, credential harvesting, and lateral movement.
The Anatomy of a Pre-Encryption Attack
According to the analysis of the GodDamn ransomware operation, the infiltration process follows a highly methodical sequence. Before a single byte of user data is encrypted, threat actors engage in a series of preparatory activities designed to maximize the impact of their eventual strike.
The research identified that attackers often start by exploiting vulnerabilities to gain initial access, subsequently establishing remote access channels. Once a foothold is established, the attackers prioritize the escalation of privileges, harvesting administrator credentials to move laterally across the network. The study revealed instances where as many as 10 distinct hosts were fully compromised and prepared for the final attack payload before the actual ransomware was executed.
This phase of "silent dwelling" allows attackers to map the network, identify high-value assets, and, in many cases, disable security software before the encryption begins. By the time a user sees a ransom note, the attacker has already achieved total visibility and control over the network’s most critical infrastructure.
Chronology of the Attack Lifecycle
The ITSEC Asia research underscores a critical timeline that IT security teams must learn to monitor. While every breach varies based on the target’s infrastructure, the "GodDamn" operation exhibits a recurring pattern:
- Initial Access and Reconnaissance: Threat actors utilize compromised remote access credentials or exploit unpatched vulnerabilities to enter the environment.
- Credential Harvesting and Privilege Escalation: Once inside, the actors deploy tools to scrape memory for credentials, allowing them to impersonate legitimate users and administrators.
- Lateral Movement and Network Discovery: Utilizing protocols such as SMB (Server Message Block) probing and ARP (Address Resolution Protocol) scanning, attackers identify interconnected devices and move from the initial entry point to broader segments of the enterprise.
- Security Evasion: Before triggering the ransomware, sophisticated actors attempt to neutralize endpoint detection and response (EDR) solutions. The report notes the alleged use of "PoisonX," a malicious kernel driver, to disrupt security monitoring processes.
- Data Exfiltration (Optional): Many modern campaigns now involve double extortion, where sensitive data is exfiltrated to cloud storage before encryption to exert further pressure on the victim.
- The Payload Execution: Finally, the ransomware is distributed across the mapped network, causing simultaneous mass encryption and rendering systems inaccessible.
Analytical Framework: Observed, Reported, and Assessed
A noteworthy aspect of the ITSEC Asia methodology is the classification of findings. To maintain academic and technical rigor, the researchers categorized their intelligence into three distinct tiers: Observed, Reported, and Assessed.
This approach is vital in an era where threat intelligence is often based on fragmentary data. By distinguishing between what was directly observed in the samples and what was reported by external, secondary sources (such as the PoisonX kernel driver, which the researchers did not independently reverse-engineer), ITSEC Asia provides a transparent view of the threat landscape. This nuance prevents the "fear-mongering" common in cybersecurity reporting and provides organizations with a realistic, evidence-based roadmap for defense.
The Strategic Shift in Defensive Posture
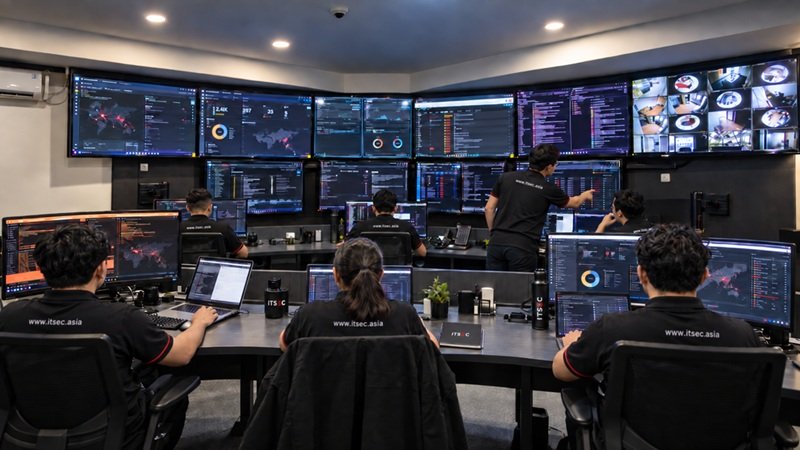
Patrick Dannacher, President Director of ITSEC Asia, emphasizes that the industry must move beyond reactive measures. "Ransomware is often detected only when the screen displays a ransom note and operations are paralyzed. However, the attacker has already spent significant time within the network gathering credentials and moving laterally," Dannacher stated.
The implications for Chief Information Security Officers (CISOs) are clear: the focus must shift from perimeter defense to behavior-based detection. Organizations are now advised to implement a "Zero Trust" architecture, where every request for access is verified regardless of whether it originates from inside or outside the network.
Key areas for improvement include:
- Enhanced Endpoint Visibility: Security teams must monitor for unusual activities, such as high-volume file modifications or the sudden disabling of security services, which serve as "early warning signals."
- Behavioral Monitoring: Automated tools should be configured to flag suspicious lateral movement patterns, such as an account accessing a server it has never interacted with before, or anomalous SMB probing.
- Immutable Backup Solutions: Since attackers often target backup systems to force victims into paying the ransom, organizations must prioritize the protection of off-site, immutable, and air-gapped backups to ensure business continuity without the need to engage with the criminals.
Broader Economic and Operational Implications
The shift toward longer, more calculated ransomware operations carries severe economic consequences. When attackers spend time mapping a network, they are not just looking for files to encrypt; they are looking for the most sensitive data—customer lists, intellectual property, and financial records—that will maximize their leverage.
The cost of a breach is no longer just the downtime required to restore systems. It now encompasses the cost of forensic investigation, legal fees, regulatory fines under frameworks like GDPR or local data privacy laws, and the long-term erosion of brand equity. The ITSEC Asia research serves as a stark reminder that if a company waits until they are locked out of their files to initiate an incident response, they have already lost the battle.
Future-Proofing Against Advanced Ransomware
As cybercriminals adopt advanced techniques—such as cross-platform capabilities that allow them to attack both Windows and Linux environments simultaneously—the need for a unified, cross-functional defense strategy becomes paramount. The ability to correlate signals from identity providers, endpoint logs, and network traffic is the only way to shorten the "dwell time" of an attacker.
The findings from the GodDamn ransomware analysis suggest that the next frontier of cybersecurity is the "pre-encryption phase." Organizations that invest in sophisticated detection capabilities during this phase, rather than focusing solely on disaster recovery, will be significantly better positioned to thwart attacks before they cause irreparable damage.
Ultimately, the takeaway for the global IT community is that ransomware is a process, not an event. By understanding the behavioral indicators—from the initial kernel-level tampering to the subtle network probing—security teams can transition from a position of vulnerability to one of active, intelligence-led defense. The era of the "unprepared victim" must come to an end, replaced by a proactive, vigilant, and highly integrated approach to digital security.