The geopolitical landscape of cybersecurity crossed a bizarre and alarming threshold when the French government officially accused the Islamic Revolutionary Guard Corps (IRGC) of Iran of orchestrating a targeted cyberattack against commercial refrigeration systems in French supermarkets. This unprecedented digital assault, which took place in October 2026, bypassed traditional targets such as government databases, financial institutions, or critical energy grids, instead opting to manipulate supermarket cooling units. The result was widespread food spoilage, forcing major retailers to discard tons of perishable goods and plunging supply chains into localized chaos. While cyber-sabotage typically targets infrastructure like power plants or water treatment facilities, the weaponization of commercial appliances highlights an evolving threat matrix where everyday infrastructure can be subverted to cause economic damage and public anxiety.
Chronology of the Cyber-Sabotage Incident
The sequence of events unfolded during a critical two-day window in mid-autumn. On October 11 and 12, 2026, numerous supermarkets across several regions in France began reporting unexplained technical malfunctions within their automated refrigeration and cooling units. Initially treated by store managers and local IT support teams as mechanical failures or software glitches, the simultaneous nature of the incidents soon raised suspicions.
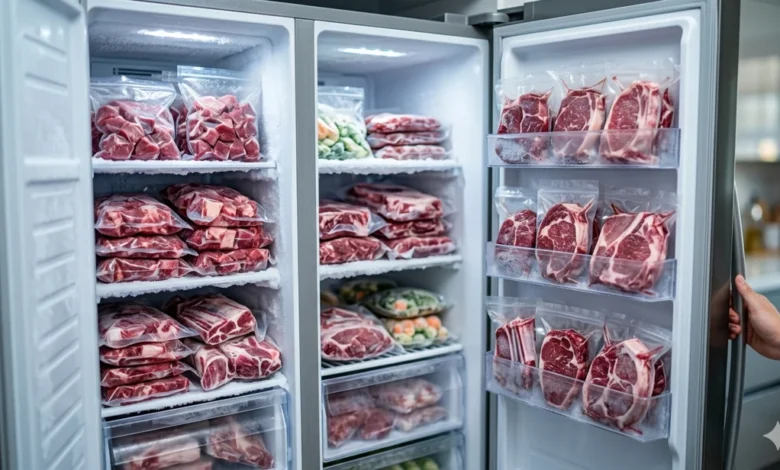
As automated temperature controls failed, internal temperatures within the display cases and storage freezers steadily rose. Because many modern commercial refrigeration systems are connected to the Internet of Things (IoT) for remote monitoring and efficiency optimization, unauthorized external actors were able to breach these networked systems. By altering the temperature settings remotely, the perpetrators ensured that perishable items—including dairy, meats, and fresh produce—were exposed to unsafe heat levels. In numerous cases, health and safety regulations forced supermarket chains to dispose of their entire inventories of perishable stock, resulting in substantial financial losses for retailers and temporary supply disruptions for consumers.
Official Accusations and French Government Response
Weeks after technical forensics and intelligence assessments were conducted, French authorities went public with their findings. French Foreign Minister Jean-Noel Barrot made a definitive statement holding Tehran directly accountable for the attack. Barrot characterized the incident as unprecedented in both its scale and its aggressive nature, emphasizing that it marked the first time a foreign actor had launched a large-scale cyber-sabotage operation aimed directly at French national territory with the intent to disrupt civilian life.
"I can confirm that this attack was carried out by the Islamic Revolutionary Guard Corps of the Islamic Republic of Iran," Barrot stated during a press briefing. He added that the assault constituted a major threat to national interests and the security of the French populace. Signaling a firm diplomatic and economic riposte, the French government announced its intention to push for stringent sanctions at the European Union level targeting all individuals and entities found responsible.
Swift diplomatic fallout ensued as the French Ministry for Europe and Foreign Affairs summoned the Iranian Ambassador to Paris to deliver a formal and severe protest. Furthermore, Paris indicated that it would pursue additional proportional measures—both through public channels and undisclosed diplomatic and intelligence avenues—to deter any future recurrence of such hybrid warfare tactics.
Judicial Investigation and Targeted Iranian Cyber Units
Beyond diplomatic reprimands, the French legal system mobilized swiftly. The Paris Public Prosecutor’s Office announced the formal opening of a judicial investigation focused on specific cyber warfare units operating under the umbrella of the Iranian military apparatus.
Paris Prosecutor Laure Beccuau detailed that the investigation centers upon the leadership of a specific Iranian cyber group known as Shahid Kaveh. According to French judicial findings, Shahid Kaveh functions as an offensive cyber unit affiliated with the Electronic and Cyber Center of the Islamic Revolutionary Guard Corps (IRGC-CEC). Warrants and investigative focus have been directed toward the top leadership of this unit, including its primary directors and two designated deputies, alongside any other individuals identified as complicit in the digital infrastructure breach.
The involvement of the IRGC is consistent with its established posture as an ideological branch of the Iranian military that has heavily invested in developing asymmetric warfare capabilities, including offensive cyber operations, over the past decade.
Tehran’s Vehement Denial and Counter-Accusations
The government of the Islamic Republic of Iran rejected the allegations from Paris, categorizing the accusations as entirely baseless, politically motivated, and lacking in credible evidence. Tehran asserted that Western governments routinely attempt to deflect attention away from domestic policy shortcomings by manufacturing external adversaries.
In an official statement released by the Iranian Ministry of Foreign Affairs, Tehran strongly condemned what it termed the obsolete policy of leveling unfounded accusations against the Iranian state. Iranian officials argued that the cyberattack narrative was being weaponized by French authorities to mask internal governance failures.
This sentiment was echoed and amplified by Iranian Foreign Minister Abbas Araghchi. Taking to social media platform X, Araghchi delivered a sharp critique of the French administration. He suggested that rather than effectively managing public services and addressing the pressing economic grievances of its own citizenry, the French government chose to scapegoat external entities for its administrative shortcomings. Despite Tehran’s rhetorical pushback, the diplomatic rift between the two nations deepened significantly following the exchange.
Broader European Union Reactions and Strategic Implications
The incident has triggered broader strategic concerns across the European Union, prompting calls for a unified and robust continental response. High Representative of the Union for Foreign Affairs and Security Policy Kaja Kallas emphasized the gravity of the situation upon being briefed on the attribution of the attack. Kallas stated that the European Union must formulate a strong and cohesive reaction to safeguard member states against emerging vectors of hybrid warfare.
Discussions among EU member states are currently underway to determine the appropriate scope of countermeasures. These deliberations are expected to focus on expanding existing EU cyber-sanction frameworks, which allow the bloc to freeze assets and impose travel bans on individuals and organizations responsible for significant cyberattacks against the Union or its member states.
The targeting of supermarket refrigeration systems represents a disturbing evolution in modern gray-zone conflicts. Historically, major state-sponsored cyber operations have targeted high-profile infrastructure such as electrical grids, financial institutions, transportation networks, and government databases. However, the exploitation of interconnected commercial appliances—often secured with weaker cybersecurity protocols than traditional critical infrastructure—illustrates a strategic shift toward asymmetric disruptions designed to erode public confidence, generate economic friction, and disrupt daily civilian commerce without crossing the threshold of conventional military conflict.
As supply chains become increasingly digitized and reliant on remote IoT management systems, incidents of this nature underscore an urgent need for heightened cybersecurity standards across the commercial and retail sectors. The ongoing investigation by French authorities, coupled with anticipated EU-wide sanctions, will likely set a crucial legal and diplomatic precedent for how nations attribute and respond to cyber-sabotage targeting civilian supply chains in the years to come.