Cyber Warfare Escalates as Ukraine and Russia Face Simultaneous Hacking of Air Raid Warning Systems

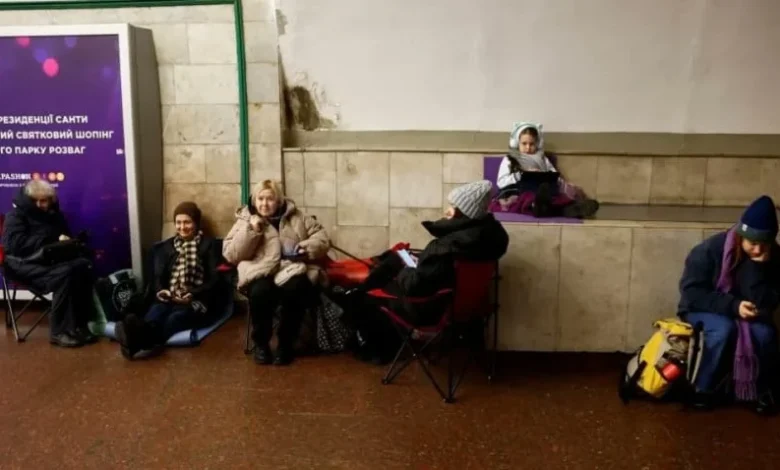
In a significant escalation of the digital theater of the ongoing conflict, both Ukraine and Russia reported coordinated cyberattacks against their respective national air raid warning applications on Sunday night. The breaches resulted in the dissemination of fraudulent, high-anxiety alerts to millions of citizens, including fabricated warnings of nuclear strikes, chemical attacks, and imminent ground combat. These incidents underscore the growing vulnerability of civil defense infrastructure to sophisticated cyber operations, transforming smartphone notifications into a battlefield for psychological warfare.
Chronology of the Cyber Incident
The disturbance began late Sunday evening when users across Ukraine reported receiving "red-level" air raid alerts through the official Air Alarm application. While these alerts are a common occurrence for the Ukrainian populace, the nature of the notifications on Sunday deviated sharply from standard protocols. Instead of generic warnings regarding incoming missile or drone trajectories, users in several regions—including the capital, Kyiv—were bombarded with spurious messages detailing radiological hazards, chemical weapon deployments, and alerts of urban street fighting.
Shortly thereafter, authorities in Russia reported a mirroring event. Users of Russian civil defense applications in various districts began receiving anomalous notifications. These messages, unlike their Ukrainian counterparts, were frequently punctuated by profanity and aggressive rhetoric, suggesting a chaotic and disruptive intent rather than a singular strategic objective. By Monday morning, both governments confirmed that their platforms had been compromised, necessitating immediate shutdowns for security audits and technical maintenance.
Contextualizing the Digital Conflict
The use of air raid warning systems as a vector for psychological operations is a logical, albeit alarming, progression in the Russia-Ukraine conflict. Since the full-scale invasion in February 2022, digital infrastructure has been a primary target for state-sponsored and hacktivist groups.
Ukraine has long relied on the "Air Alarm" app, developed by Ajax Systems and Stfalcon with the support of the Ministry of Digital Transformation, to disseminate real-time warnings. The app is a critical tool for public safety, integrated with official state military data to provide rapid alerts. For the Russian side, similar applications serve both as public safety tools and, occasionally, as conduits for state-mandated narratives.
The fact that both systems were targeted within hours of one another raises significant questions regarding the sophistication of the attackers. While no group has claimed responsibility, security analysts have pointed to the complexity of breaching these localized, state-hardened systems. Whether the attacks were the work of a single entity employing a "tit-for-tat" strategy or two independent groups capitalizing on similar vulnerabilities remains the subject of ongoing forensic investigations.
Official Responses and Mitigation Efforts
The response from Kyiv was immediate and aimed at de-escalating the public panic caused by the false alarms. The Ukrainian Air Force issued a statement via their official Telegram channel, explicitly clarifying the situation for the public. "The Air Alarm application may have been subjected to enemy interference," the statement read. "There is no threat of radiation! Remain calm and follow our updates on our official channels."
The Ukrainian government moved to temporarily deactivate the application to conduct a comprehensive security review. The authorities noted that the false messages were written in Russian, which served as an immediate "red flag" for many Ukrainian users, providing a degree of skepticism that mitigated some of the intended mass hysteria.
In Russia, the reaction was more subdued but equally urgent. Local municipal authorities confirmed that the disruption was under investigation and cautioned citizens to rely solely on verified, government-issued bulletins. The breach of the Russian system, which included vulgar language, suggests that the attackers may have been seeking to undermine the perceived authority and discipline of the state’s emergency messaging apparatus.
Supporting Data and Technical Vulnerabilities
The incident highlights a broader trend in global cyber warfare: the weaponization of civilian alert systems. Security experts have previously warned that mobile notification systems—which are designed for speed and reach—often lack the robust end-to-end encryption or multi-factor authentication protocols required to prevent sophisticated spoofing.
According to data from cybersecurity think tanks, there has been a 300% increase in cyber incidents targeting critical infrastructure in Eastern Europe since 2022. These attacks are generally categorized into three types:
- DDoS Attacks: Designed to overwhelm servers and render the apps useless.
- Defacement: Modifying the interface to display propaganda.
- Data Infiltration: Accessing the backend to push false alerts, as seen in this instance.
The vulnerability exploited in this case appears to be related to the API (Application Programming Interface) gateways that connect the military’s command-and-control centers to the consumer-facing mobile applications. By compromising these gateways, attackers can bypass the verification checks typically required to trigger a nationwide alert.
Strategic Implications and Psychological Impact
The primary goal of such an attack is not necessarily to cause physical harm, but to erode public trust in government communication. When a citizen can no longer trust their emergency notification app, the effectiveness of the civil defense system is compromised. If a real attack were to occur in the future, the "crying wolf" effect—where citizens ignore or delay their response to alerts due to past false alarms—could lead to a significantly higher casualty rate.
Furthermore, the psychological impact of receiving a notification about a nuclear strike on a smartphone cannot be overstated. In an environment already marked by chronic stress and trauma, these incidents are designed to induce panic, drain the emotional reserves of the population, and create a sense of total insecurity.
From a geopolitical perspective, the simultaneous nature of these attacks serves as a reminder that the digital front of the war is borderless. The ability to reach millions of individuals in their homes, in both Kyiv and Moscow, illustrates that no population is entirely removed from the reach of cyber adversaries.
Future Resilience and Policy Analysis
As both nations move to patch their systems, the focus will likely shift toward "zero-trust" architectures. This involves implementing stricter authentication measures for any user or process attempting to push information to the public.
Policy analysts suggest that this incident will serve as a catalyst for new international norms regarding the protection of civilian warning systems. Historically, the Geneva Convention and other international frameworks have struggled to keep pace with digital warfare. However, the targeting of non-combatant populations through false emergency information could lead to renewed calls for treating such systems as protected infrastructure, similar to hospitals or power grids.
For now, the situation serves as a grim case study in the vulnerability of modern digital society. The integration of technology into the core of civil defense provides unprecedented speed and accessibility, but it also creates a singular point of failure that, when exploited, can cause national-level distress.
Conclusion
The dual-hacking incident on Sunday is a stark illustration of the evolving nature of the Russia-Ukraine war. While the physical front lines remain locked in a grueling battle, the digital front continues to expand, reaching into the private lives of millions. The rapid recovery of these systems is a testament to the resilience of the technical teams involved, yet the psychological toll on the public remains a persistent challenge.
As forensic experts continue to examine the logs and entry points of the breach, the global community will be watching closely. The lessons learned from this incident will likely influence how nations protect their citizens in the digital age, emphasizing that in a time of war, the most dangerous weapon is often the one that tells you exactly what you fear most. Whether these attacks were intended to be a mere nuisance or a trial run for more destructive cyber operations, they have fundamentally altered the landscape of public safety communication in conflict zones. Both Ukraine and Russia are now faced with the task of rebuilding the sanctity of the information they provide to their citizens, ensuring that when the siren sounds, it is not merely a digital phantom, but a signal to seek safety.